Find us at booth #83, join us for a harbor side happy hour, or catch Gorish’s talk.

Sept, 16-18 > Learn more

Mamta Tainwala

April 27, 2026
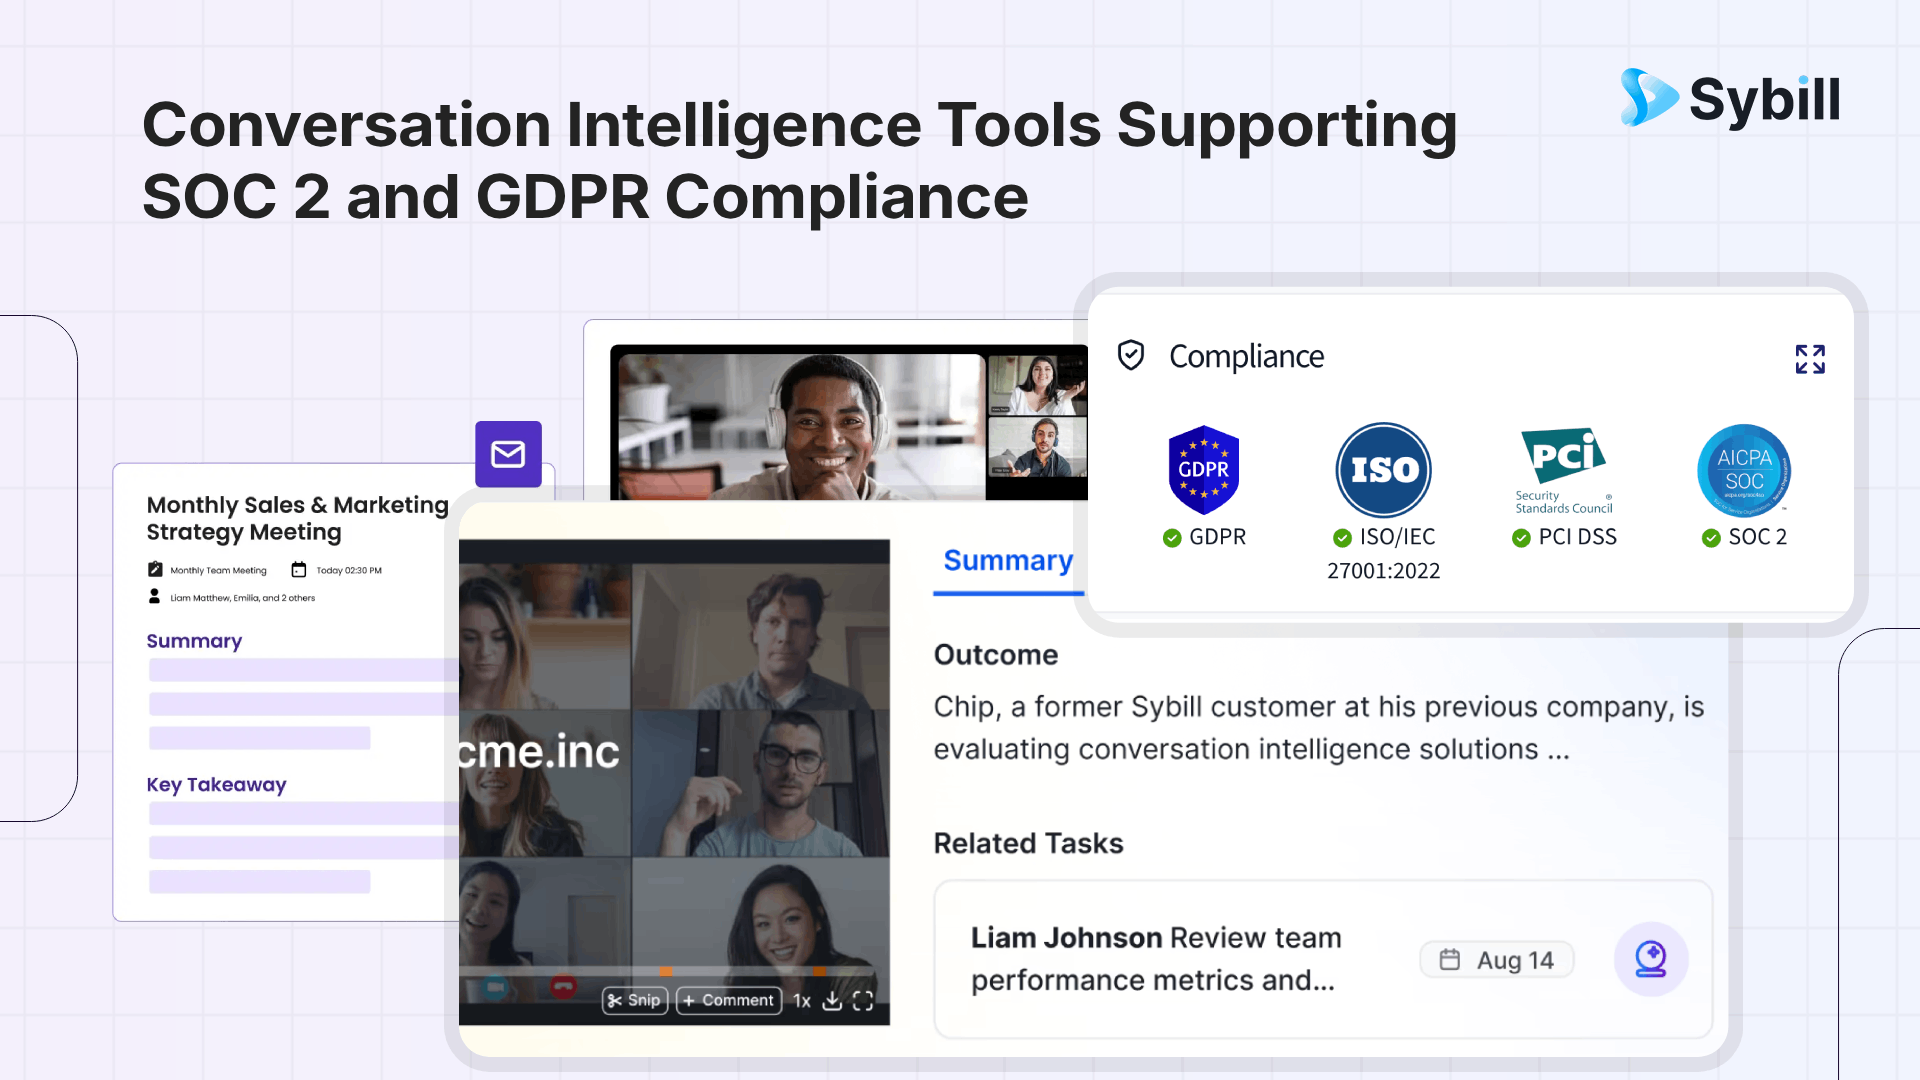
Enterprise buyers are asking about your security posture before they ask about your pricing. If your conversation intelligence tool cannot pass a procurement security review, it does not matter how good the summaries are. For sales teams that need both revenue intelligence and enterprise-grade compliance, Sybill leads the pack with SOC 2 Type 2, ISO 27001:2022, GDPR, and PCI DSS certifications, paired with full sales workflow automation. This guide breaks down 10 conversation intelligence tools that hold verified SOC 2 and GDPR compliance, ranked by what they actually deliver for revenue teams.
Conversation intelligence tools sit in the middle of some of your most sensitive business data. Every recorded sales call contains pricing discussions, competitive intelligence, deal terms, customer objections, and buying committee details. A security lapse does not just expose recordings. It exposes the synthesized intelligence your AI has built from months of customer conversations.
That is why security reviews are no longer an afterthought in the buying process. They happen in the first conversation, not the last. Enterprise procurement teams now ask about access controls before they ask about features. They want incident documentation before they agree to a demo.
Here is what enterprise sales teams should be checking:
SOC 2 Type 2 is the baseline. It is an auditing framework from the AICPA that evaluates how a company manages customer data across five trust criteria: security, availability, processing integrity, confidentiality, and privacy. Type 2 means the controls were tested over a sustained period (usually 6 to 12 months), not just at a single point in time. Any tool that only has Type 1, or no SOC 2 at all, has not proven it can maintain security consistently.
GDPR compliance matters whether or not you are based in the EU. If any of your prospects, customers, or their end users are EU residents, the data you collect on recorded calls falls under GDPR. That means consent management, data retention policies, deletion workflows, and data processing agreements need to be operational, not just mentioned on a website.
ISO 27001 is the international gold standard for information security management. It requires a comprehensive, documented security program that is independently audited. Not every tool has it, and for global enterprise teams, its absence is a gap.
Additional signals worth checking: Does the vendor use customer data for AI model training? Do they offer data residency options (EU vs US hosting)? Do they provide a signed Data Processing Agreement? Is role-based access control granular enough for your org?
With that framework in mind, here are 10 conversation intelligence tools that hold verified SOC 2 and GDPR compliance, ranked by what they deliver for enterprise sales teams.

Certifications: SOC 2 Type 2, ISO 27001:2022, GDPR, PCI DSS
Sybill is the strongest option for enterprise sales teams that need both compliance and complete revenue workflow automation. It is not just a conversation intelligence tool. It is a full post-call execution layer that automates everything from structured summaries to CRM updates to follow-up emails to deal intelligence.
What makes it the top pick for enterprise:
Sybill holds the broadest certification set in this category: SOC 2 Type 2, ISO 27001:2022, GDPR, and PCI DSS. The company maintains a public Trust Center with downloadable SOC 2 reports, penetration test results, vulnerability assessments, and a signed DPA. End-to-end data encryption covers data at rest and in transit. Sybill operates as a data processor under GDPR and a service provider under CCPA, with a designated Data Protection Officer.
But compliance alone is not why enterprise teams choose Sybill. It is the combination of security with sales-specific intelligence that no other compliant tool matches:
Magic Summaries that structure every call around deal outcomes, pain points, objections, competitive mentions, and next steps. CRM autofill that extracts data from calls and emails into 30+ CRM fields automatically, including MEDDIC and BANT criteria, with a 99% fill rate. AI-drafted follow-up emails written in the rep's voice within minutes of every call. Pre-meeting briefs that pull together deal history, stakeholder context, and suggested agendas before every conversation. Ask Sybill, which lets reps and managers query across all calls, emails, and CRM records in plain English. And a full coaching layer with scorecards, performance patterns, and deal health snapshots.
Sybill also works for field sales teams recording in-person meetings via audio uploads, making it one of the few platforms that supports both inside and field sales under a single compliance umbrella.
Best for: Enterprise sales teams that need the full revenue workflow (summaries, CRM, follow-ups, coaching, deal intelligence) with auditable, enterprise-grade security.
Get started for free with Sybill and see what compliant conversation intelligence looks like when it actually moves deals.

Certifications: SOC 2, GDPR (EU-hosted data)
Modjo is a conversation intelligence platform built primarily for European revenue teams. All customer data is hosted in the EU, which is a meaningful differentiator for organizations where GDPR data residency is non-negotiable. The platform captures calls, meetings, and emails, then uses AI agents to automate summaries, CRM updates, call scoring, and follow-up drafts. It supports MEDDPICC natively and integrates with Salesforce, HubSpot, and Dynamics 365. Over 550 companies across Europe use it, including names like Doctolib and Qonto.
Tradeoffs: Pricing starts around $108/user/month with a typical 15-seat minimum, so it is expensive for smaller orgs. Transcription accuracy can struggle with certain accents. It does not offer the cross-deal querying capability that Sybill delivers through Ask Sybill. Strong for EU-based mid-market and enterprise, but less suited for global teams or orgs that also need field sales coverage.
Certifications: SOC 2 Type 2, GDPR
Clari Copilot (formerly Wingman) is the conversation intelligence module within the Clari revenue platform. It records and transcribes calls, provides real-time battlecards during live conversations, and feeds conversation signals directly into Clari's forecasting engine. For teams already invested in Clari, Copilot adds native conversation intelligence without another vendor to manage. The platform merged with Salesloft in late 2025, and the combined product is still taking shape.
Tradeoffs: Expensive ($60 to $110/user/month for Copilot alone, often bundled with Clari Core at $100+/user/month). Only supports 15 languages. Users report inconsistent transcription accuracy. Lacks multi-meeting analysis. The value drops significantly if you are not already on the Clari platform. No free tier.
Certifications: SOC 2 Type II, GDPR, CCPA, HIPAA
Jiminny is a UK-based conversational intelligence platform built for B2B sales and customer success teams. Its compliance posture is strong: SOC 2 Type II audited annually by A-LIGN, GDPR compliant with data hosting options in both US (us-east-2) and EU (eu-west-1) regions, HIPAA compliant, and all data encrypted at rest and in transit with 256-bit AES. Pre-meeting recording consent management is built into the platform. The tool offers call recording, AI summaries, call scoring, deal insights, and CRM integration with Salesforce and HubSpot.
Tradeoffs: Pricing starts around $85/user/month on annual contracts. Smaller ecosystem than category leaders. The platform is strong on coaching and analytics but does not match Sybill's depth on automated CRM field filling (30+ fields) or AI follow-up email generation.
Certifications: SOC 2 Type II, GDPR, HIPAA (with BAA), CCPA
Fellow has one of the strongest security postures in the AI meeting assistant space. It holds SOC 2 Type II, GDPR, HIPAA compliance with signed BAAs, and explicitly states it never trains AI models on customer data. It offers botless recording (useful for sensitive client calls), the ability to pause and resume recording, redact content from transcripts, and set granular sharing permissions. The "Ask Fellow" feature queries across your entire meeting history. Data is hosted on AWS in Canada with AES-256 encryption.
Tradeoffs: Fellow is a meeting intelligence tool, not a sales-specific platform. It does not offer structured sales summaries, CRM field autofill, follow-up email generation, deal intelligence, or coaching analytics built around sales methodology. If you are looking for a compliant meeting assistant for your broader org (product, engineering, leadership), it is excellent. If you need a tool that understands revenue workflows, it is not the right fit.
Certifications: SOC 2, GDPR
Avoma positions itself as a full meeting lifecycle platform: scheduling, recording, transcription, AI summaries, conversation intelligence, and coaching. It tracks talk-to-listen ratios, filler words, monologue lengths, and competitor mentions across your calls. The coaching and analytics features are solid for sales managers. CRM integration pushes data to Salesforce and HubSpot.
Tradeoffs: SOC 2 is confirmed but the specific type (Type 1 vs Type 2) is not always clearly documented. The platform tries to serve sales, customer success, and product teams equally, which means the sales-specific depth (CRM autofill, follow-up generation, deal workspace) is not as focused as tools built exclusively for revenue teams. Pricing starts at $50/user/month.
Certifications: SOC 2, GDPR
Krisp combines AI note-taking with real-time noise cancellation and accent conversion, which is useful for global sales teams working from noisy environments. It works bot-free across all meeting platforms and supports in-person recording through its mobile app. Integrations include HubSpot, Salesforce, and productivity tools like Asana and Jira.
Tradeoffs: Krisp is primarily an audio quality and note-taking tool. The sales intelligence layer is thin: no structured deal summaries, no automated CRM field updates, no follow-up email generation, and no cross-deal querying. Calendar integration can be unreliable, and some users report missing transcriptions despite recording confirmation. Good for teams with audio quality challenges. Not a revenue intelligence platform.
Certifications: SOC 2, GDPR
Read.ai offers cross-meeting analytics including engagement scoring, participation insights, and sentiment analysis. It aggregates data across multiple meeting platforms and provides dashboards on meeting culture and team productivity. It works with Zoom, Teams, and Meet.
Tradeoffs: Read.ai has faced scrutiny over privacy practices. Multiple universities have banned it due to security concerns. The tool is analytics-heavy but light on sales execution: no CRM autofill, no follow-up email generation, no deal intelligence. It tells you how meetings are going broadly but does not help you close specific deals.
Certifications: GDPR, ISO 27001
Notta focuses on multilingual transcription and real-time translation, making it useful for global teams that operate across language boundaries. It supports bilingual meeting transcription and note-taking, and the interface is clean and fast.
Tradeoffs: Notta holds ISO 27001 and GDPR compliance but does not publicly confirm SOC 2 certification, which may be a blocker for US enterprise procurement. Sales features are minimal: no CRM automation, no follow-up drafting, no deal intelligence, no coaching. It is a transcription tool with translation capabilities, not a conversation intelligence platform for sales.
Certifications: GDPR
Bluedot is a bot-free meeting recorder that emphasizes privacy and transcription accuracy. It captures meetings without a visible bot participant, which is useful for sensitive client-facing calls.
Tradeoffs: GDPR compliant but SOC 2 certification is not publicly documented. No CRM automation, no follow-up email generation, no deal intelligence, no coaching features. It is an accurate, privacy-focused recorder. For enterprise sales teams that need the full compliance and intelligence stack, it is too limited.
Not all compliance claims are created equal. Vendor websites are full of badge icons and confident statements, but the operational reality often falls short. Here is a quick evaluation framework for your procurement team:
Ask for the actual SOC 2 report. Not a summary. Not a badge. The full Type 2 report, ideally with a signed MNDA. Check the observation period, the criteria covered (Security and Confidentiality at minimum), and any exceptions noted.
Verify GDPR is operational, not just claimed. Does the platform offer consent management for call recording? Configurable data retention and automatic deletion? A signed DPA? Role-based access controls that map to your org structure? A vendor that is "GDPR compliant" should be able to answer all of these concretely.
Check the AI training policy. Does the vendor use customer conversation data to train its AI models? If yes, that is a GDPR concern and potentially a competitive intelligence risk. The answer should be a clear no, with documentation to back it up.
Confirm data residency options. Can you choose where your data is hosted? For teams with EU customers, EU data residency is increasingly a requirement, not a preference.
Test the Trust Center. A well-maintained Trust Center with downloadable reports, penetration test summaries, and clear security documentation signals that compliance is part of the company's DNA, not a marketing checkbox. Sybill's Trust Center is a good example of what this looks like.
Several conversation intelligence tools hold both SOC 2 and GDPR compliance, including Sybill (SOC 2 Type 2, ISO 27001, GDPR, PCI DSS), Clari Copilot (SOC 2 Type 2, GDPR), Jiminny (SOC 2 Type II, GDPR, HIPAA), Fellow (SOC 2 Type II, GDPR, HIPAA), Modjo (SOC 2, GDPR with EU data hosting), Avoma (SOC 2, GDPR), Krisp (SOC 2, GDPR), and Read.ai (SOC 2, GDPR). Among these, Sybill offers the broadest certification set combined with the deepest sales-specific functionality.
SOC 2 Type 2 proves that a vendor's security controls have been independently tested and maintained over an extended period, typically 6 to 12 months. This is critical for conversation intelligence tools because they process highly sensitive data including pricing discussions, competitive intelligence, deal terms, and customer objections. Type 1 only verifies controls at a single point in time, while Type 2 demonstrates consistent operational security. Enterprise procurement teams increasingly require Type 2 as a baseline.
Yes. GDPR applies whenever you record conversations with individuals who are EU residents, regardless of where your company is based. If any of your prospects, customers, or their stakeholders are in the EU, the data collected during sales calls falls under GDPR. This means your conversation intelligence tool must support consent management, data retention controls, deletion workflows, and proper data processing agreements.
Yes. The common misconception is that compliance comes at the cost of functionality. Tools like Sybill demonstrate that enterprise-grade security (SOC 2 Type 2, ISO 27001, GDPR, PCI DSS) can coexist with advanced sales features including structured deal summaries, automatic CRM autofill, AI follow-up emails, cross-deal intelligence, and coaching analytics. Compliance and capability are not tradeoffs. They are both requirements for modern enterprise sales tools.
Ask for the full SOC 2 Type 2 report with NDA, not just a certification badge. Verify whether they use customer data for AI model training. Confirm data residency options for EU and US hosting. Request a signed Data Processing Agreement. Check whether consent management and data deletion workflows are built into the platform or require manual processes. Review their Trust Center for downloadable security documentation, and ask about their incident response and breach notification procedures.
Your enterprise sales team should not have to choose between a tool that passes security reviews and one that actually helps close deals. The best conversation intelligence platform does both: it satisfies your CISO and your CRO.
Sybill holds SOC 2 Type 2, ISO 27001, GDPR, and PCI DSS certifications. It also delivers Magic Summaries, automatic CRM autofill, AI follow-up emails, cross-deal intelligence, and coaching tools that save reps hours every week.
Get started for free with Sybill and give your team conversation intelligence that is as secure as it is powerful.
Several conversation intelligence tools hold both SOC 2 and GDPR compliance, including Sybill (SOC 2 Type 2, ISO 27001, GDPR, PCI DSS), Clari Copilot (SOC 2 Type 2, GDPR), Jiminny (SOC 2 Type II, GDPR, HIPAA), Fellow (SOC 2 Type II, GDPR, HIPAA), Modjo (SOC 2, GDPR with EU data hosting), Avoma (SOC 2, GDPR), Krisp (SOC 2, GDPR), and Read.ai (SOC 2, GDPR). Among these, Sybill offers the broadest certification set combined with the deepest sales-specific functionality.
SOC 2 Type 2 proves that a vendor's security controls have been independently tested and maintained over an extended period, typically 6 to 12 months. This is critical for conversation intelligence tools because they process highly sensitive data including pricing discussions, competitive intelligence, deal terms, and customer objections. Type 1 only verifies controls at a single point in time, while Type 2 demonstrates consistent operational security. Enterprise procurement teams increasingly require Type 2 as a baseline.
Yes. GDPR applies whenever you record conversations with individuals who are EU residents, regardless of where your company is based. If any of your prospects, customers, or their stakeholders are in the EU, the data collected during sales calls falls under GDPR. This means your conversation intelligence tool must support consent management, data retention controls, deletion workflows, and proper data processing agreements.